Hi there, I’m Eshan.
A Cybersecurity Enthusiast and Web Developer from Bharat. I excel in securing digital assets and creating innovative web solutions.
Featured Projects
Projects Showcase
Explore my recent cybersecurity tools and web applications.
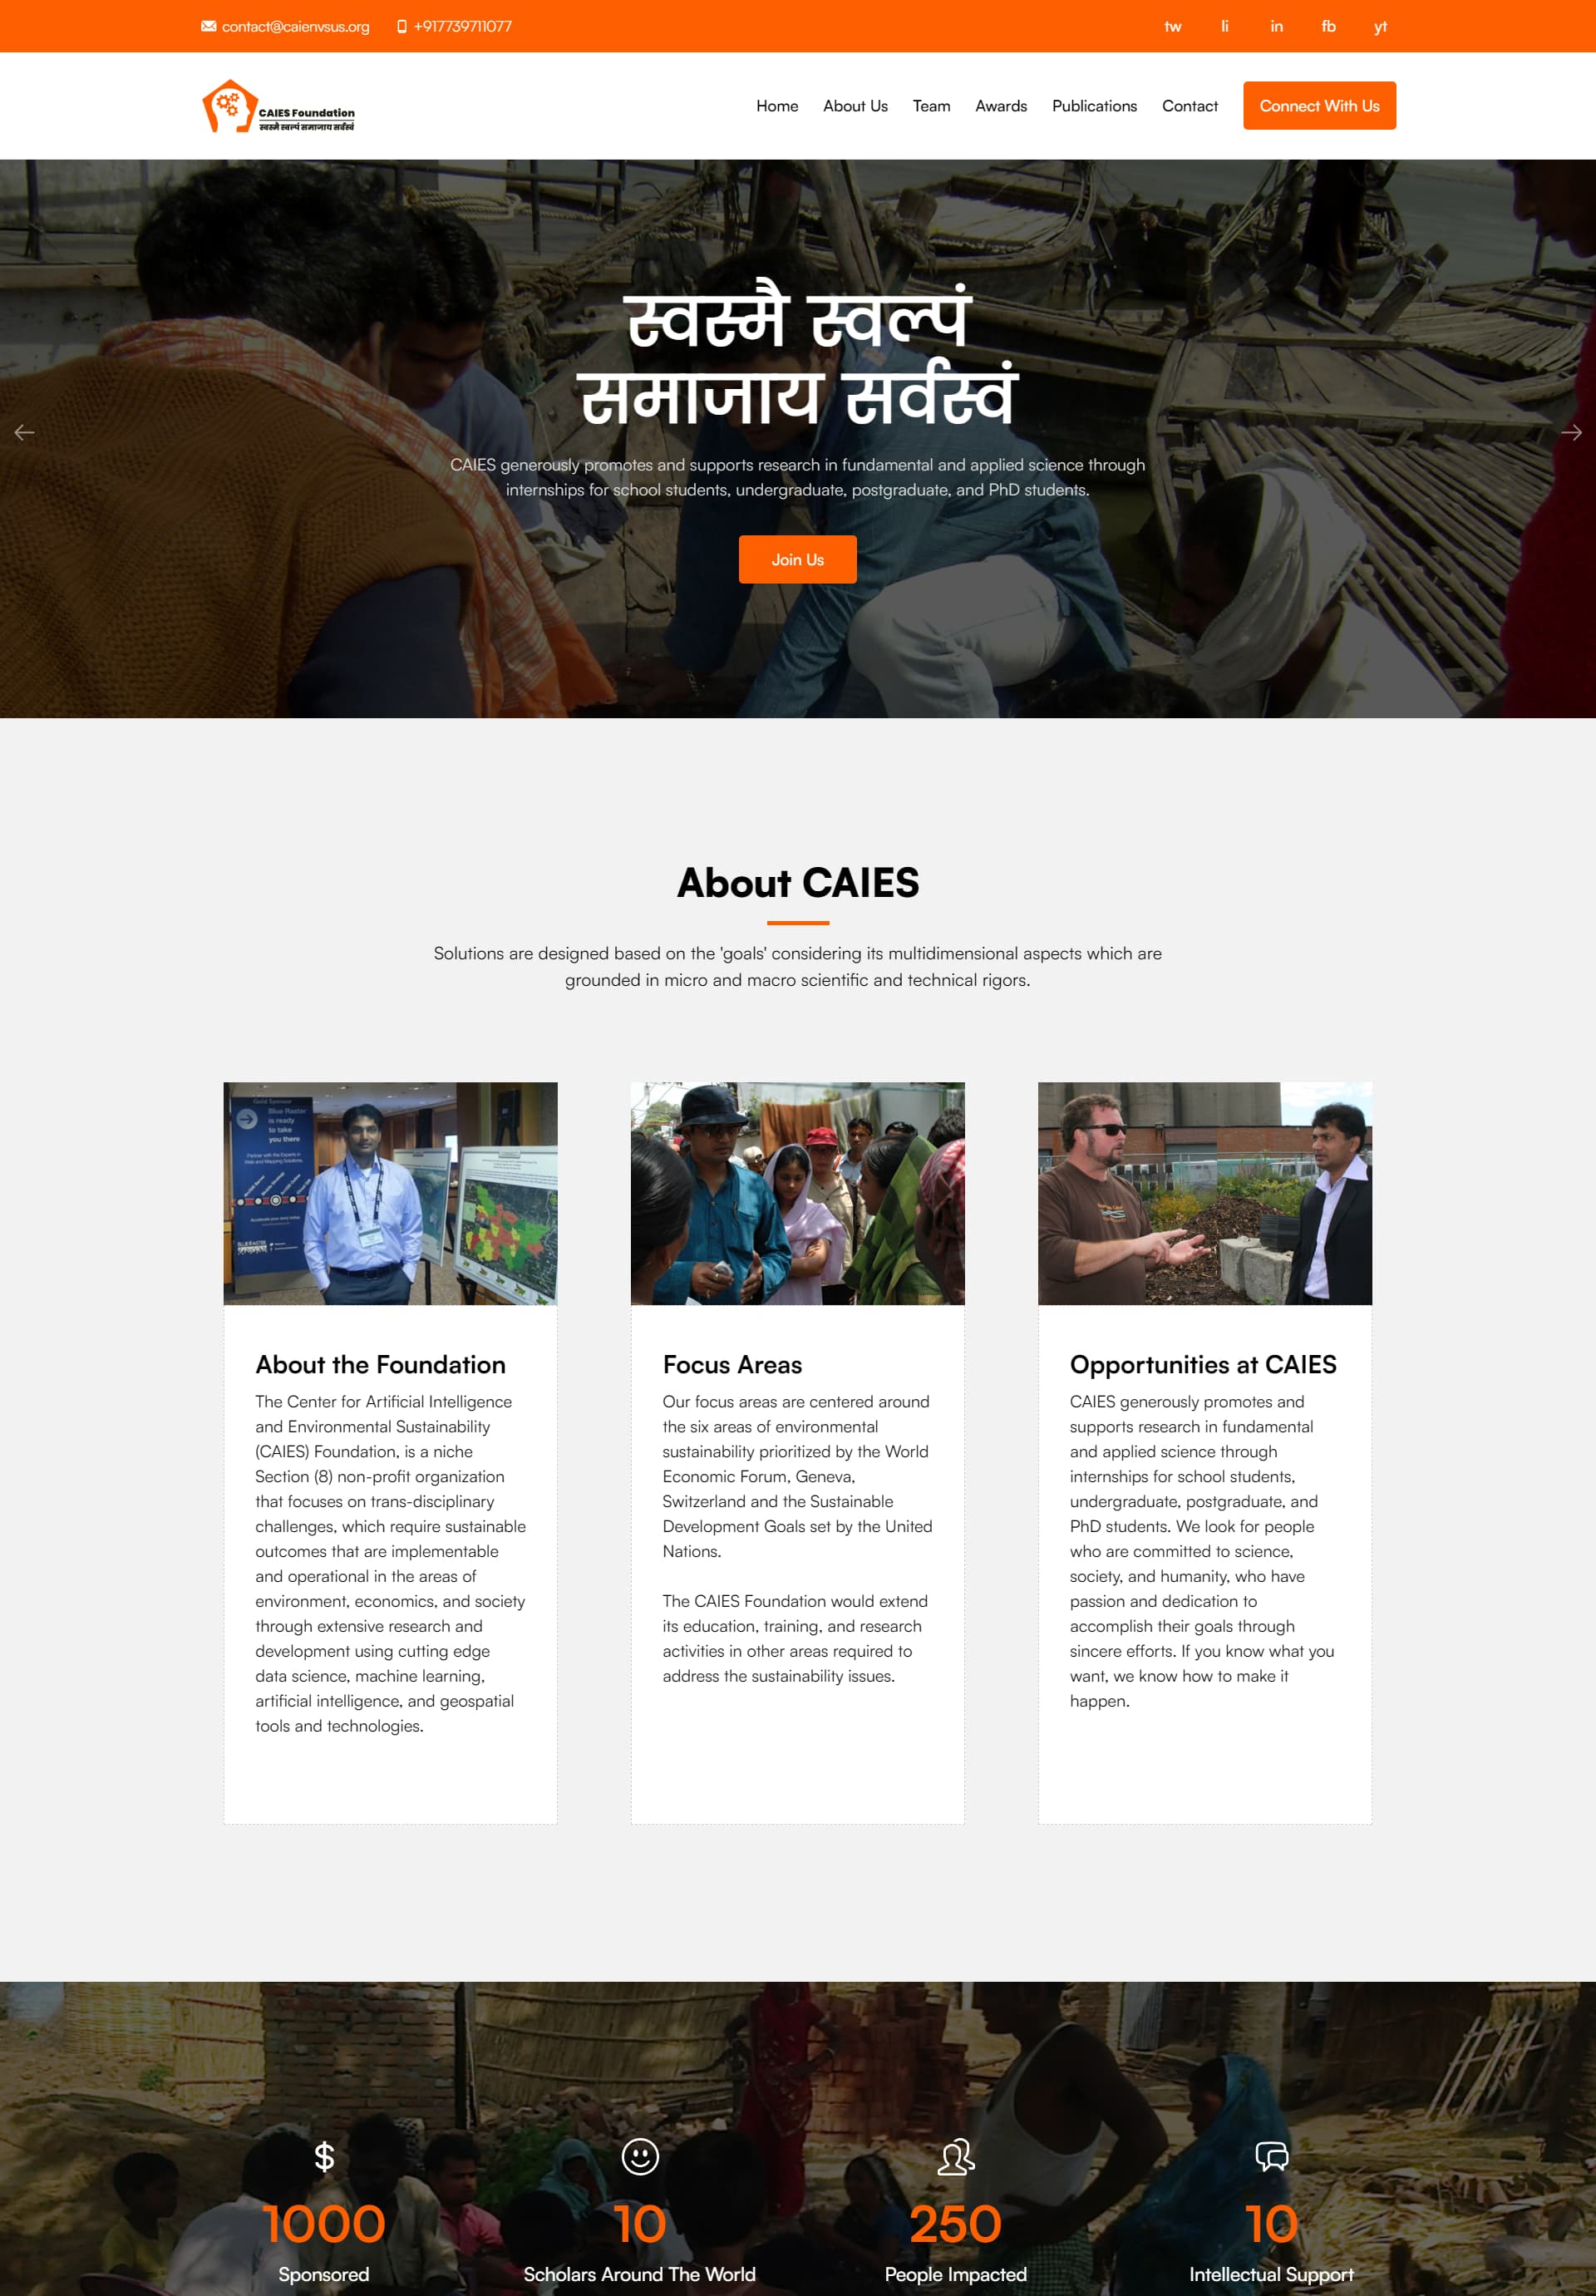
CAIES Foundation Website
The Center for Artificial Intelligence and Environmental Sustainability (CAIES) Foundation, is a niche Section (8) non-profit organization that focuses on trans-disciplinary challenges, which require sustainable outcomes that are implementable and operational in the areas of environment, economics, and society through extensive research and development using cutting edge data science, machine learning, artificial intelligence, and geospatial tools and technologies.
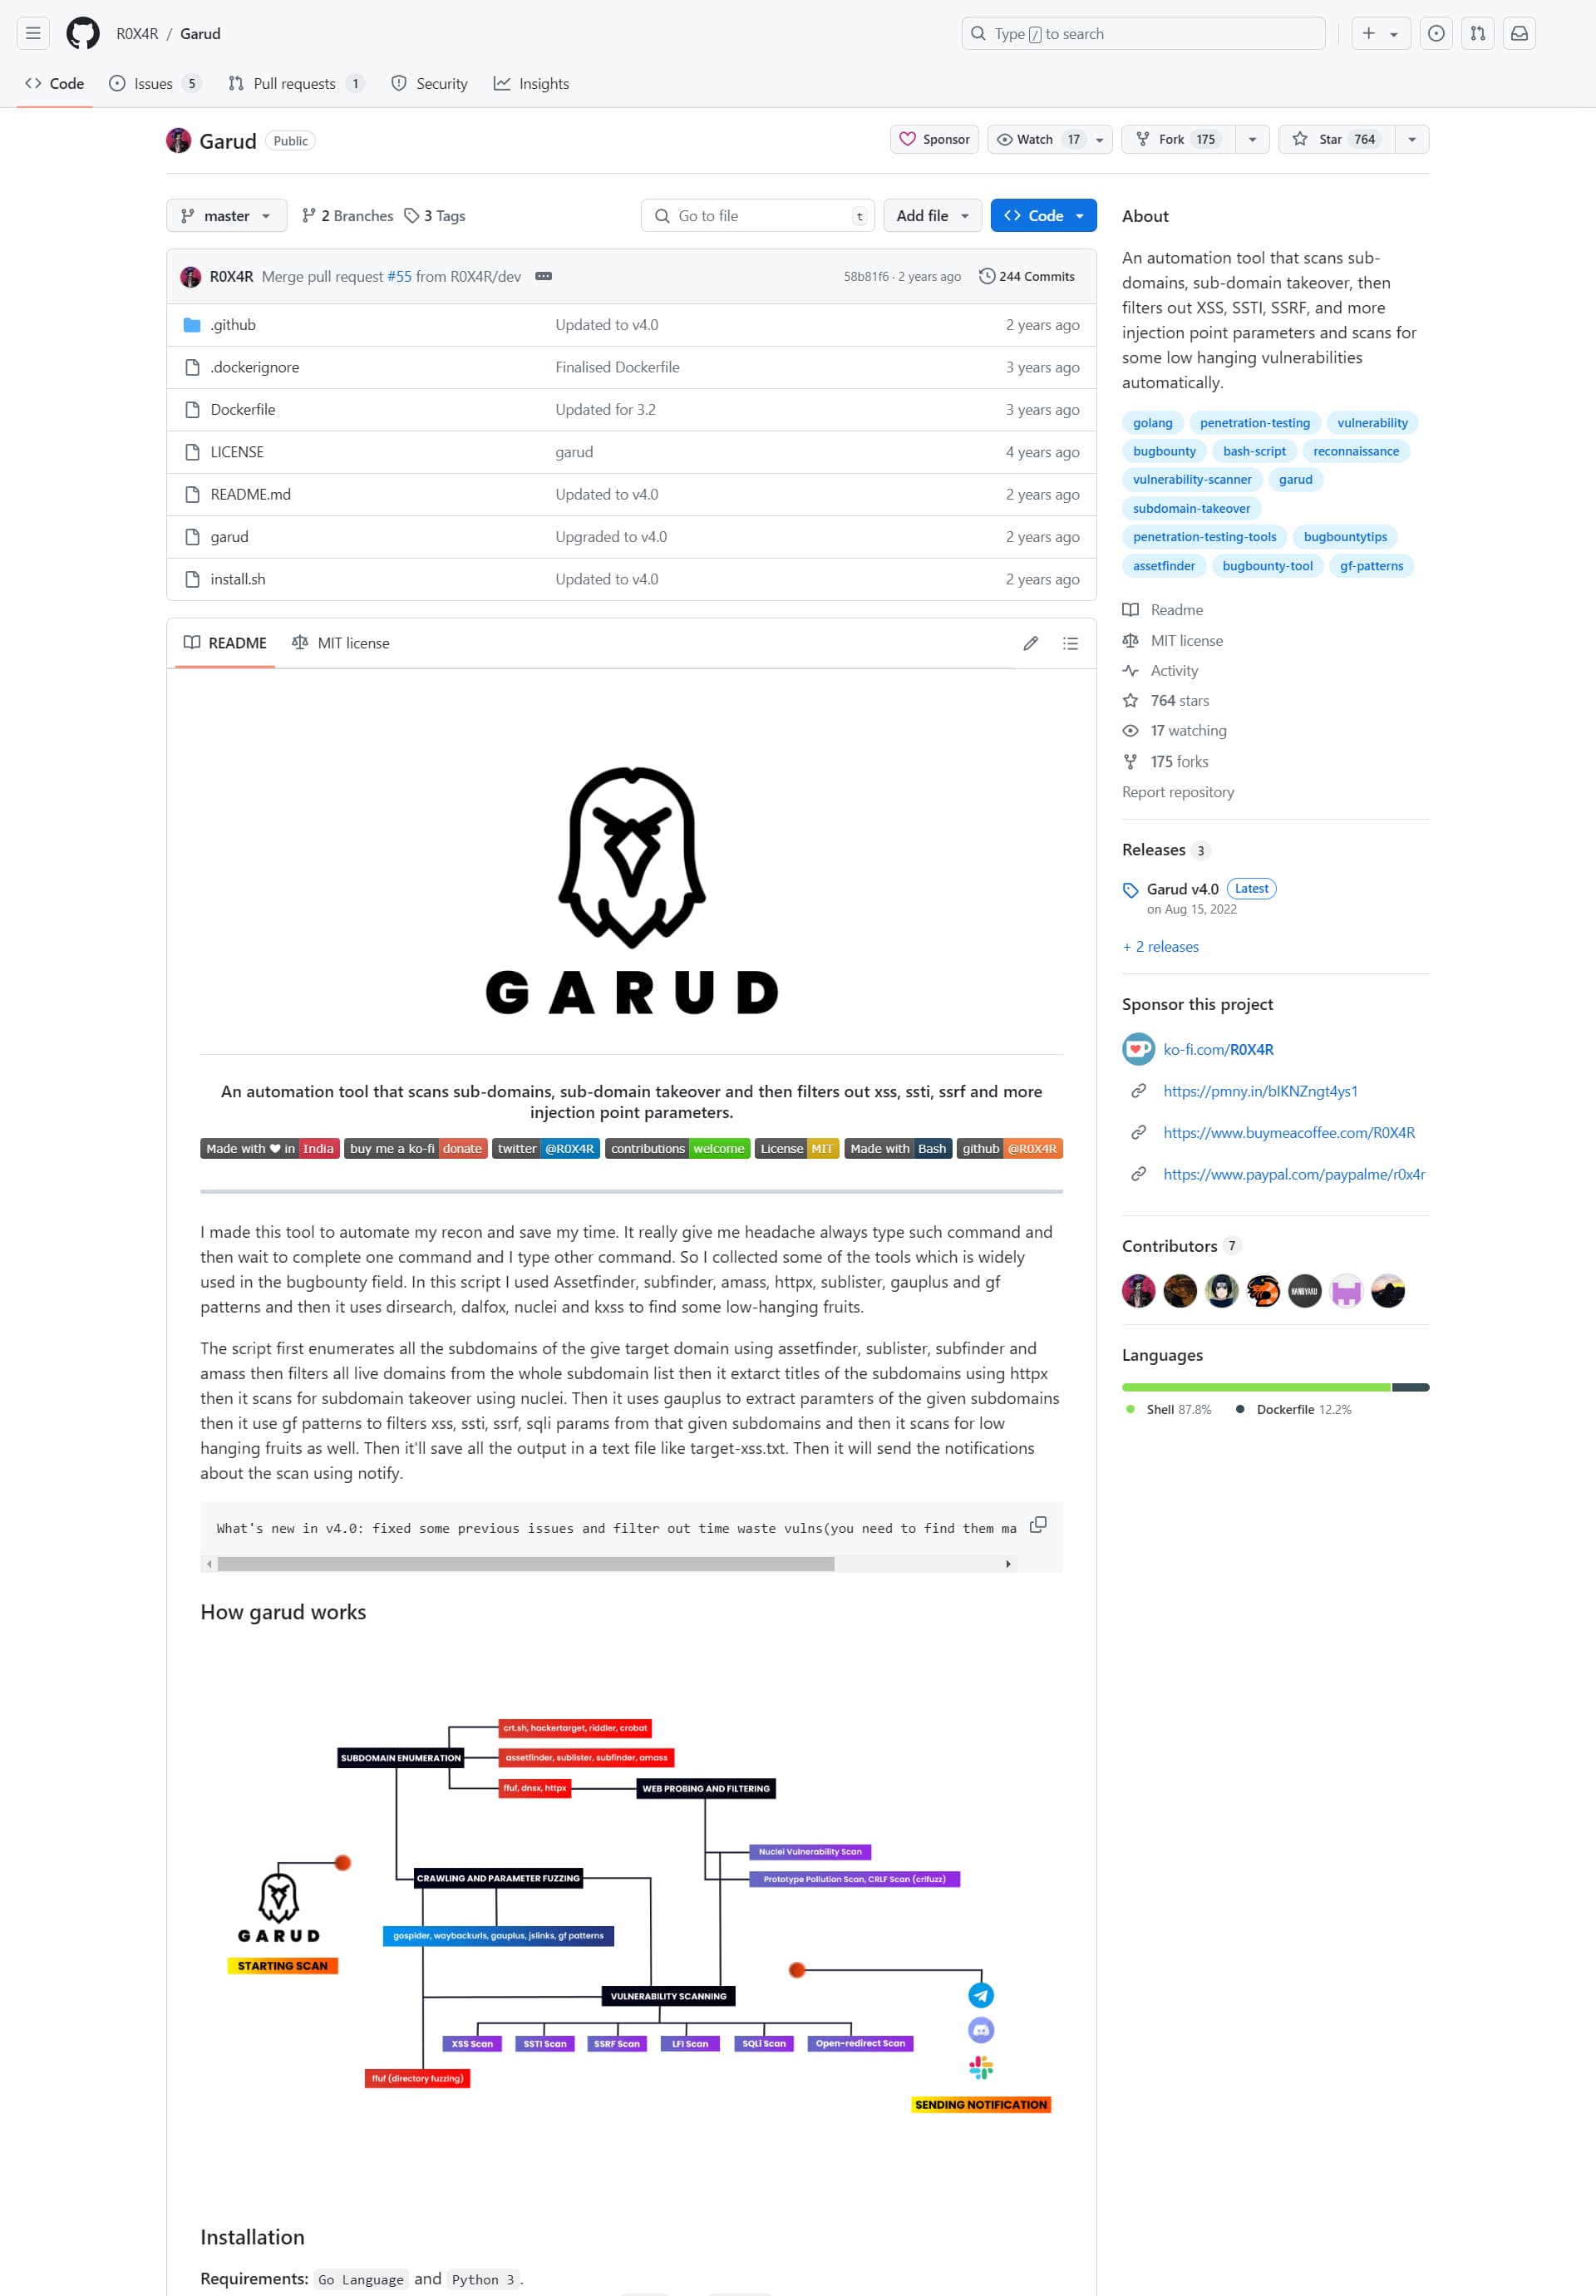
Garud
An automation tool that scans sub-domains, sub-domain takeover, then filters out XSS, SSTI, SSRF, and more injection point parameters and scans for some low hanging vulnerabilities automatically.
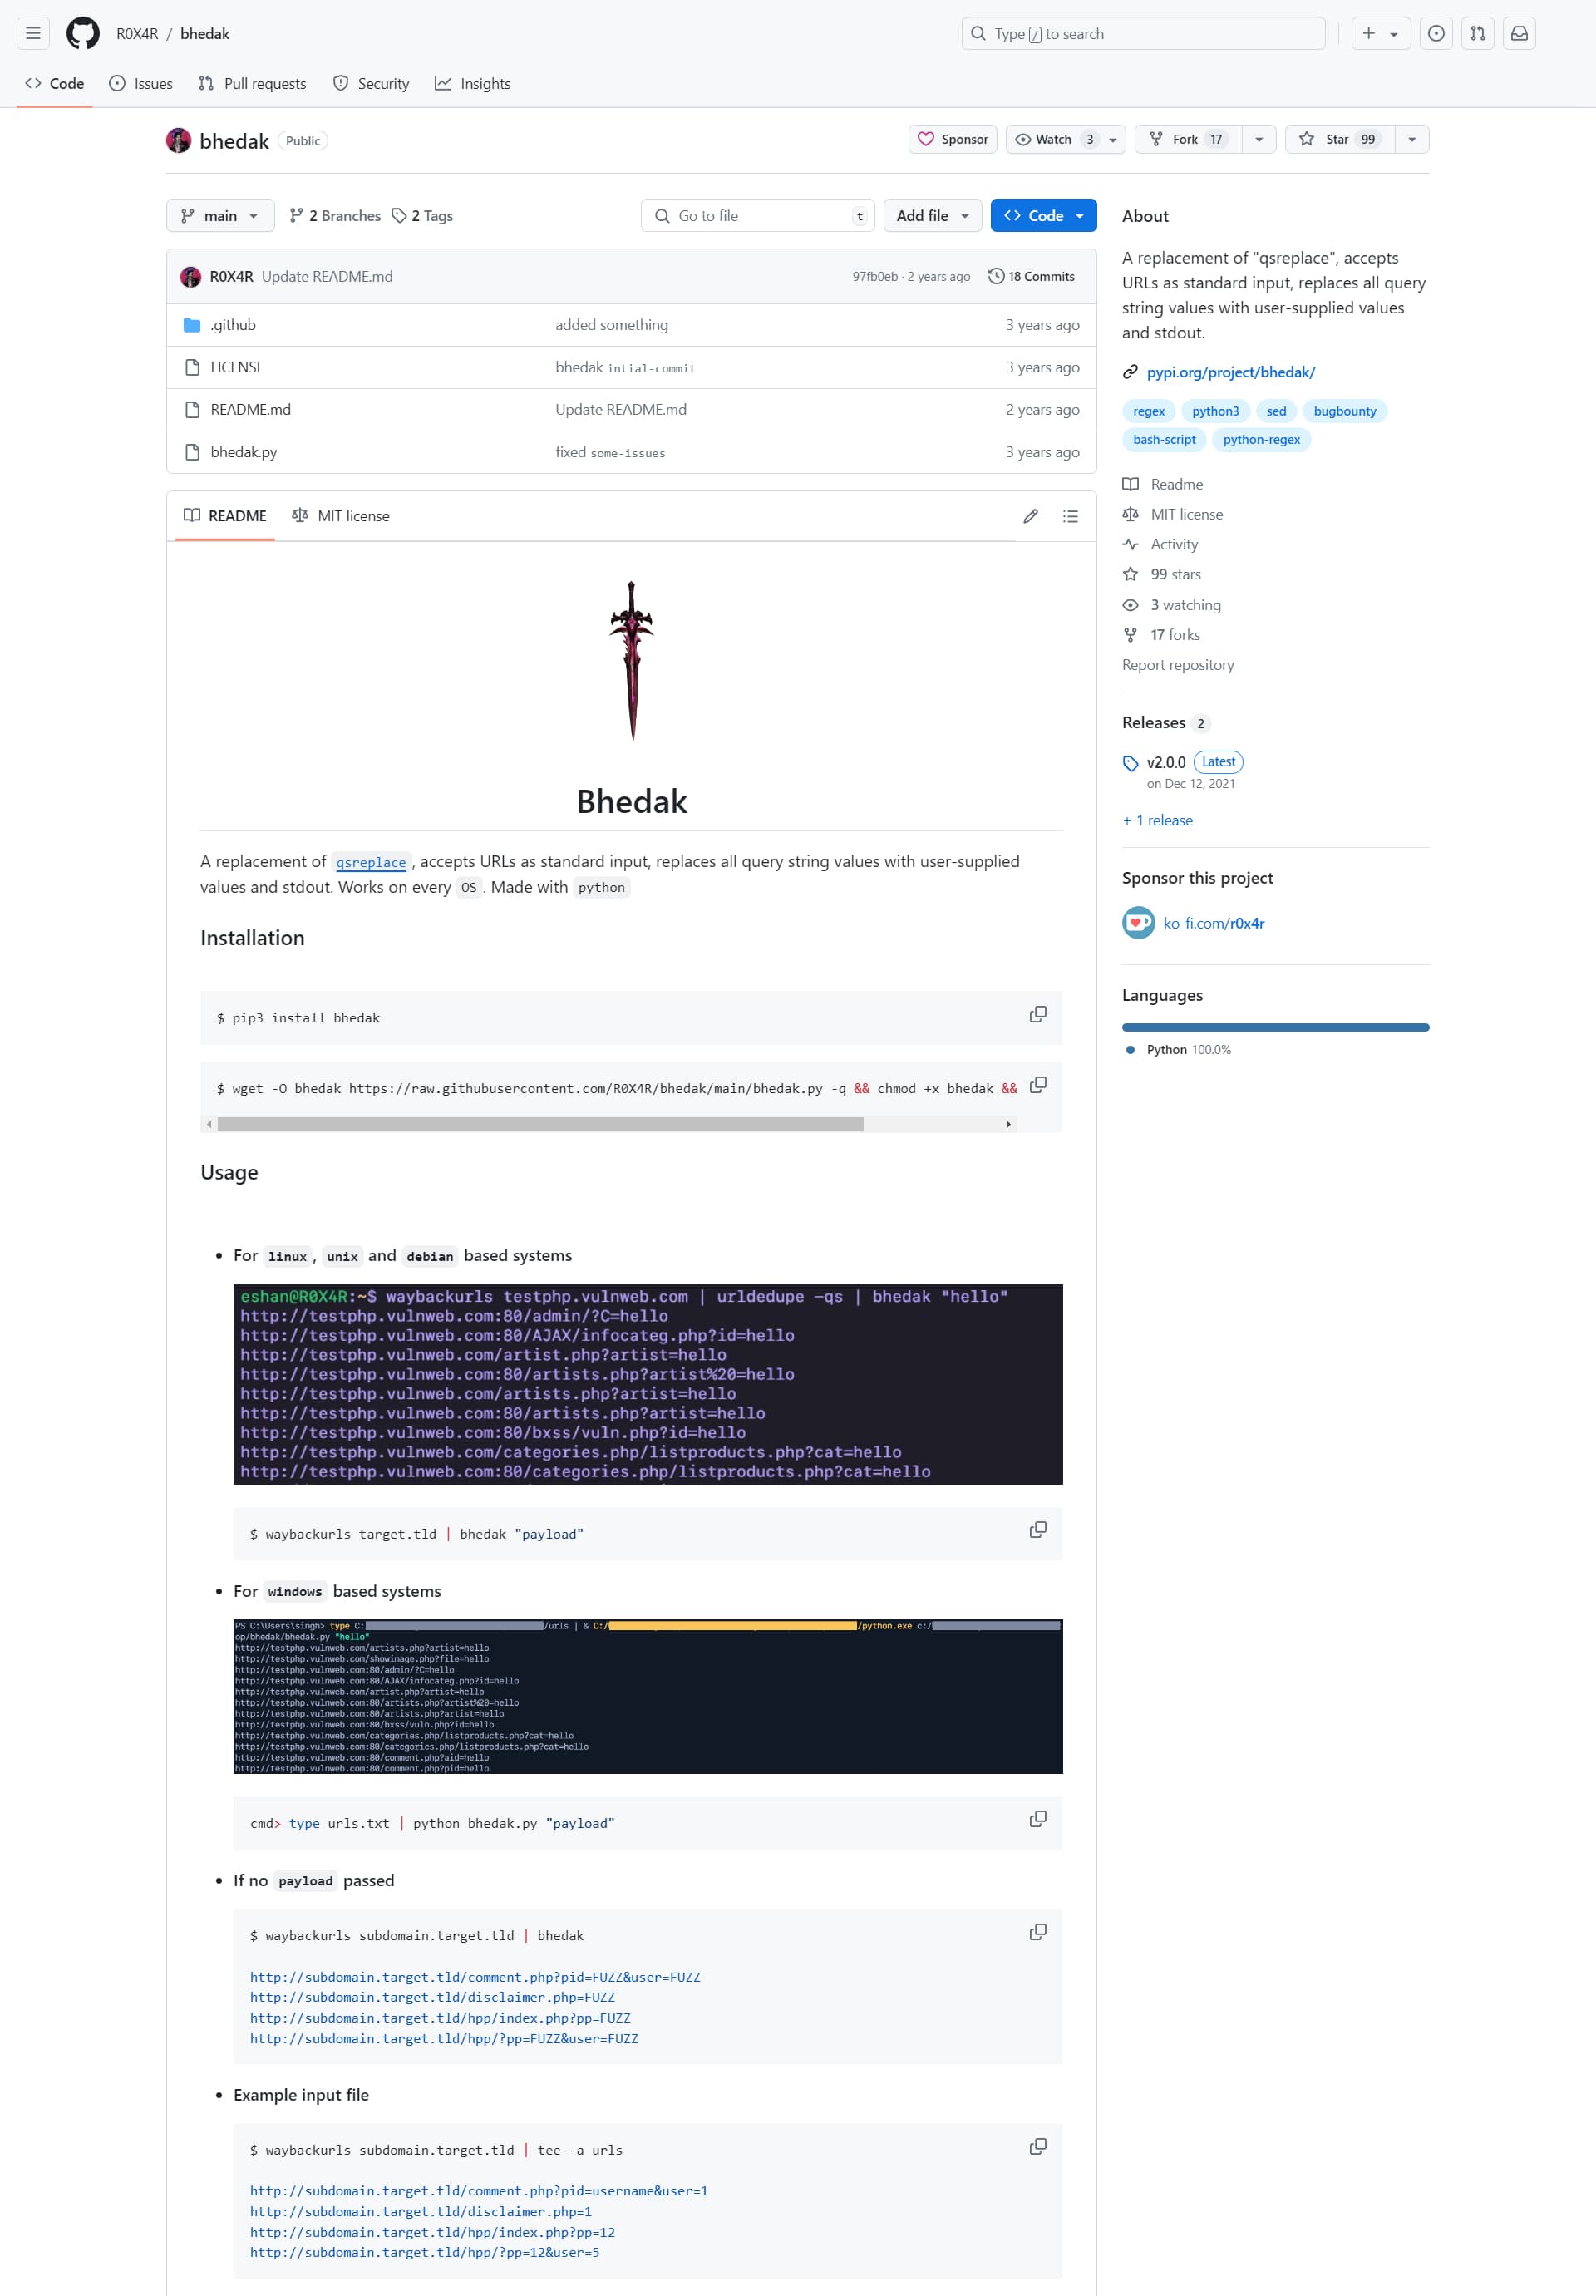
Bhedak
A replacement of qsreplace, accepts URLs as standard input, replaces all query string values with user-supplied values and stdout. Works on every OS. Made with python
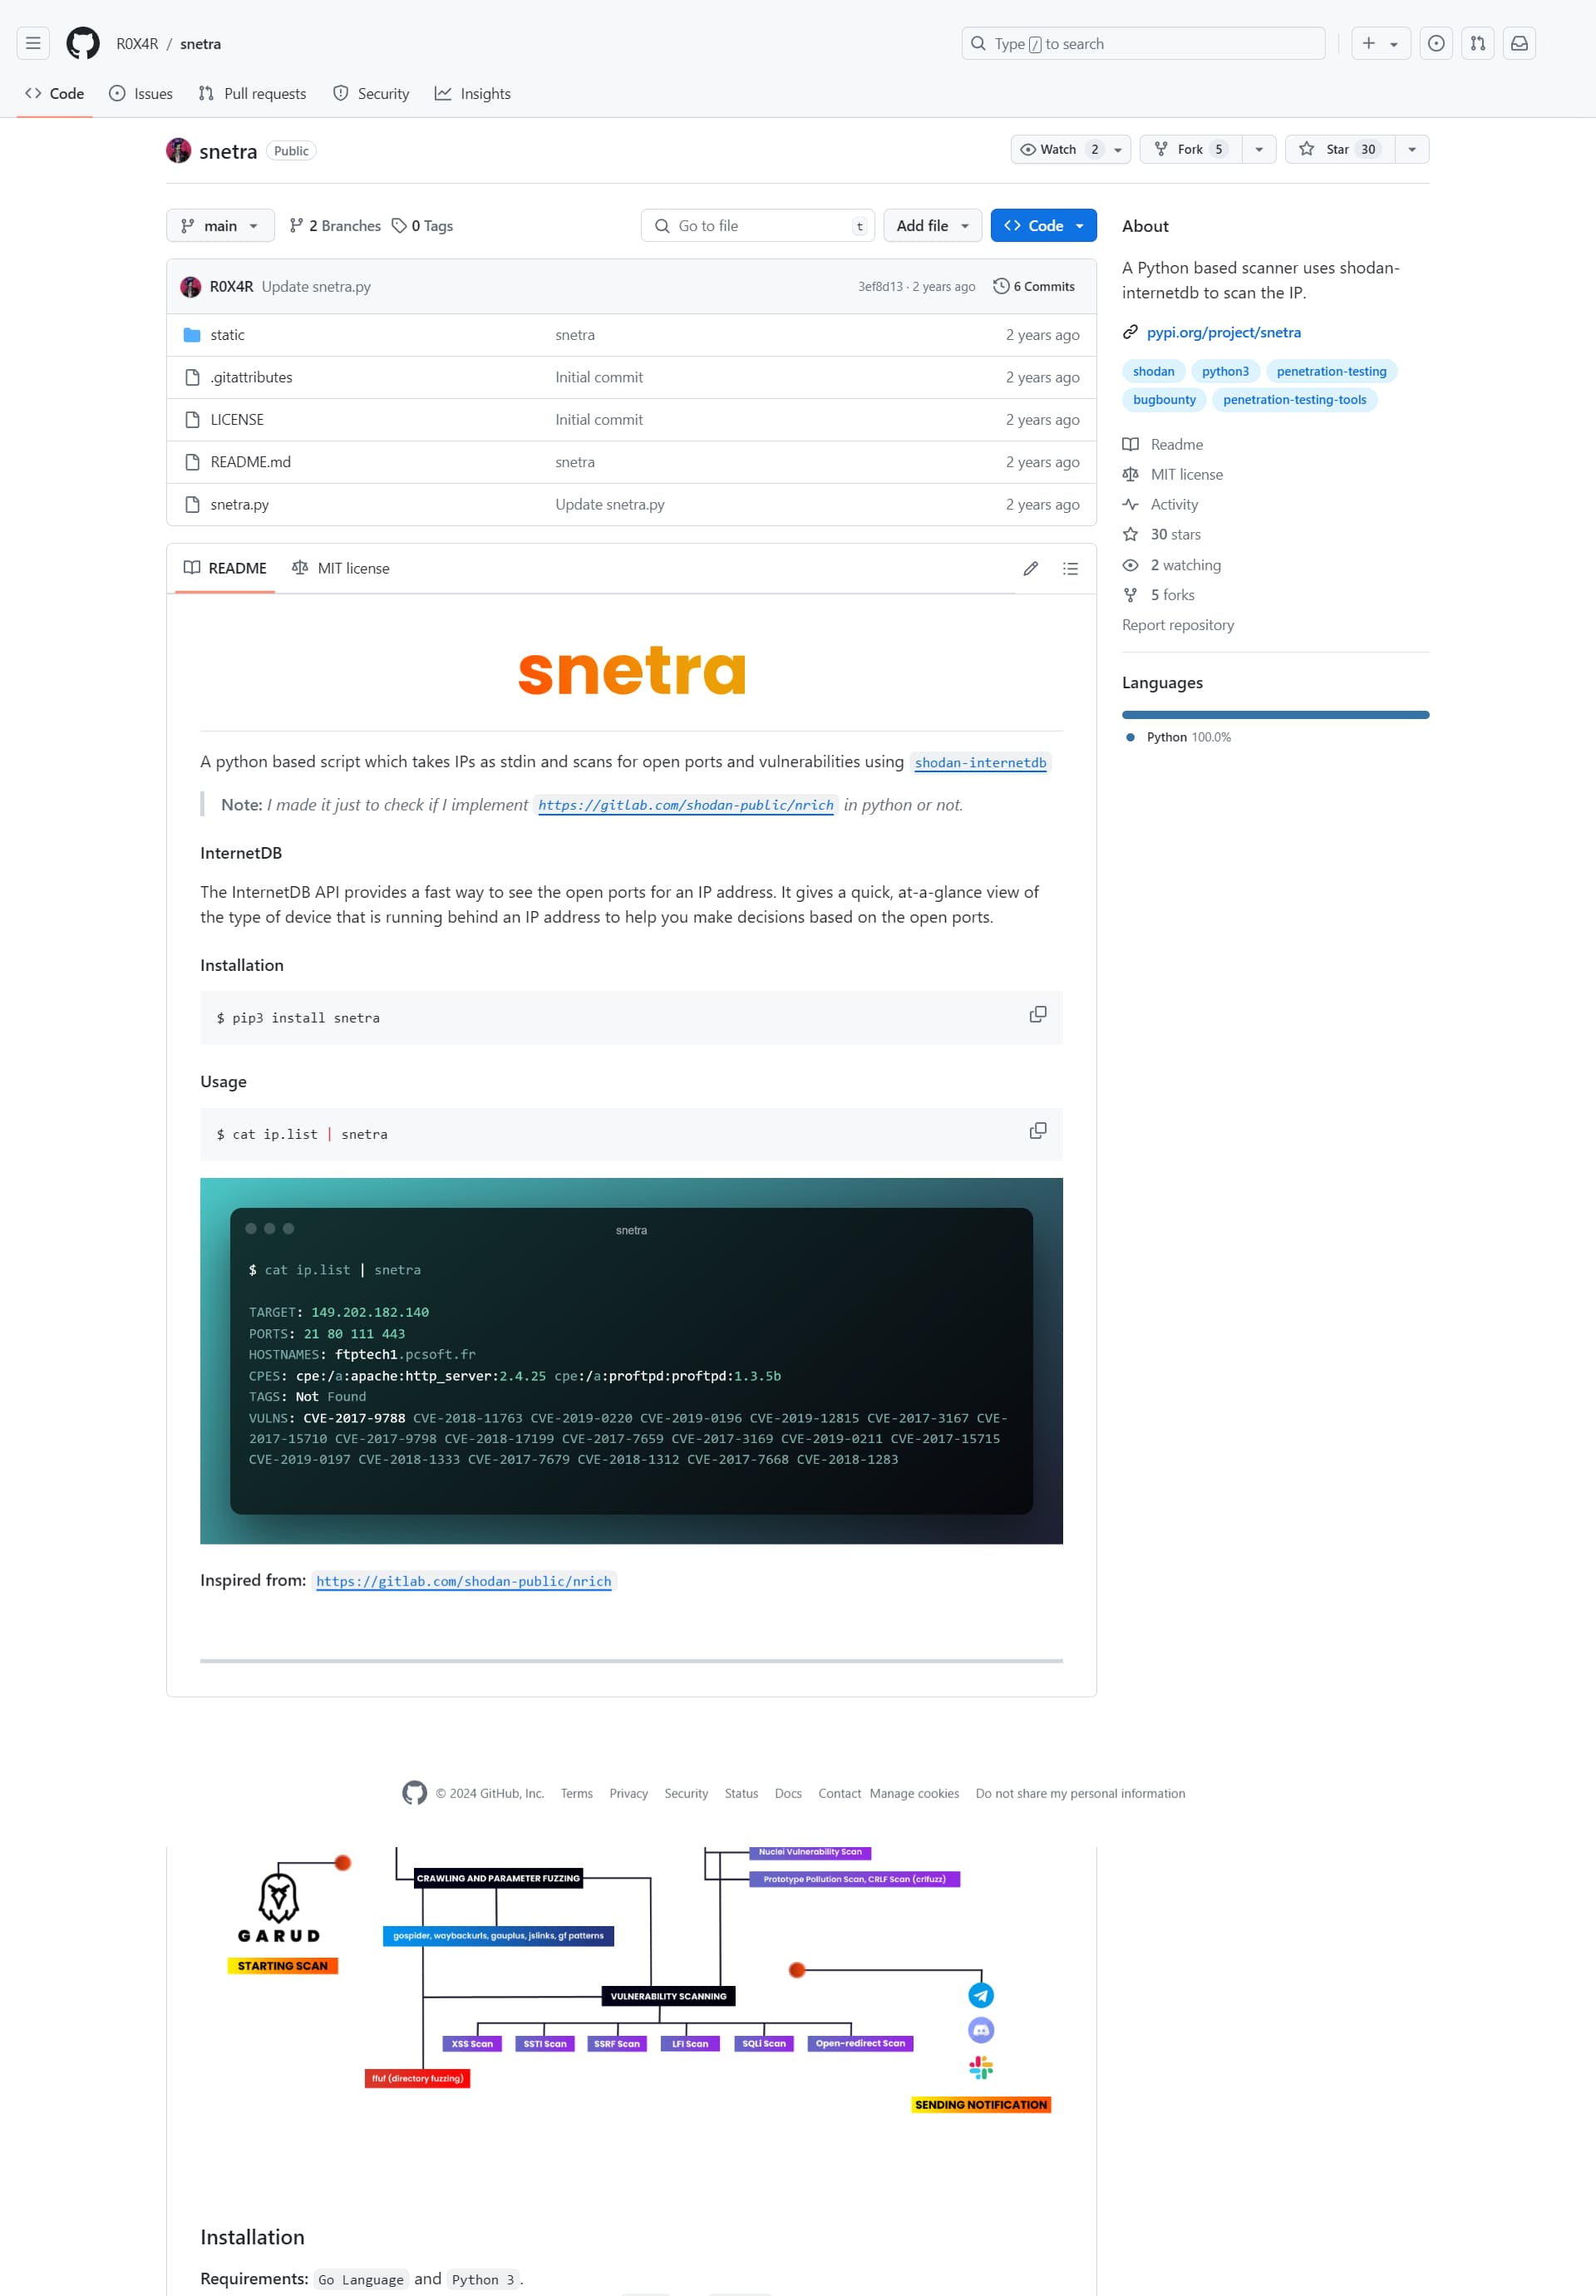
Snetra
A Python based scanner uses shodan-internetdb to scan the IP.
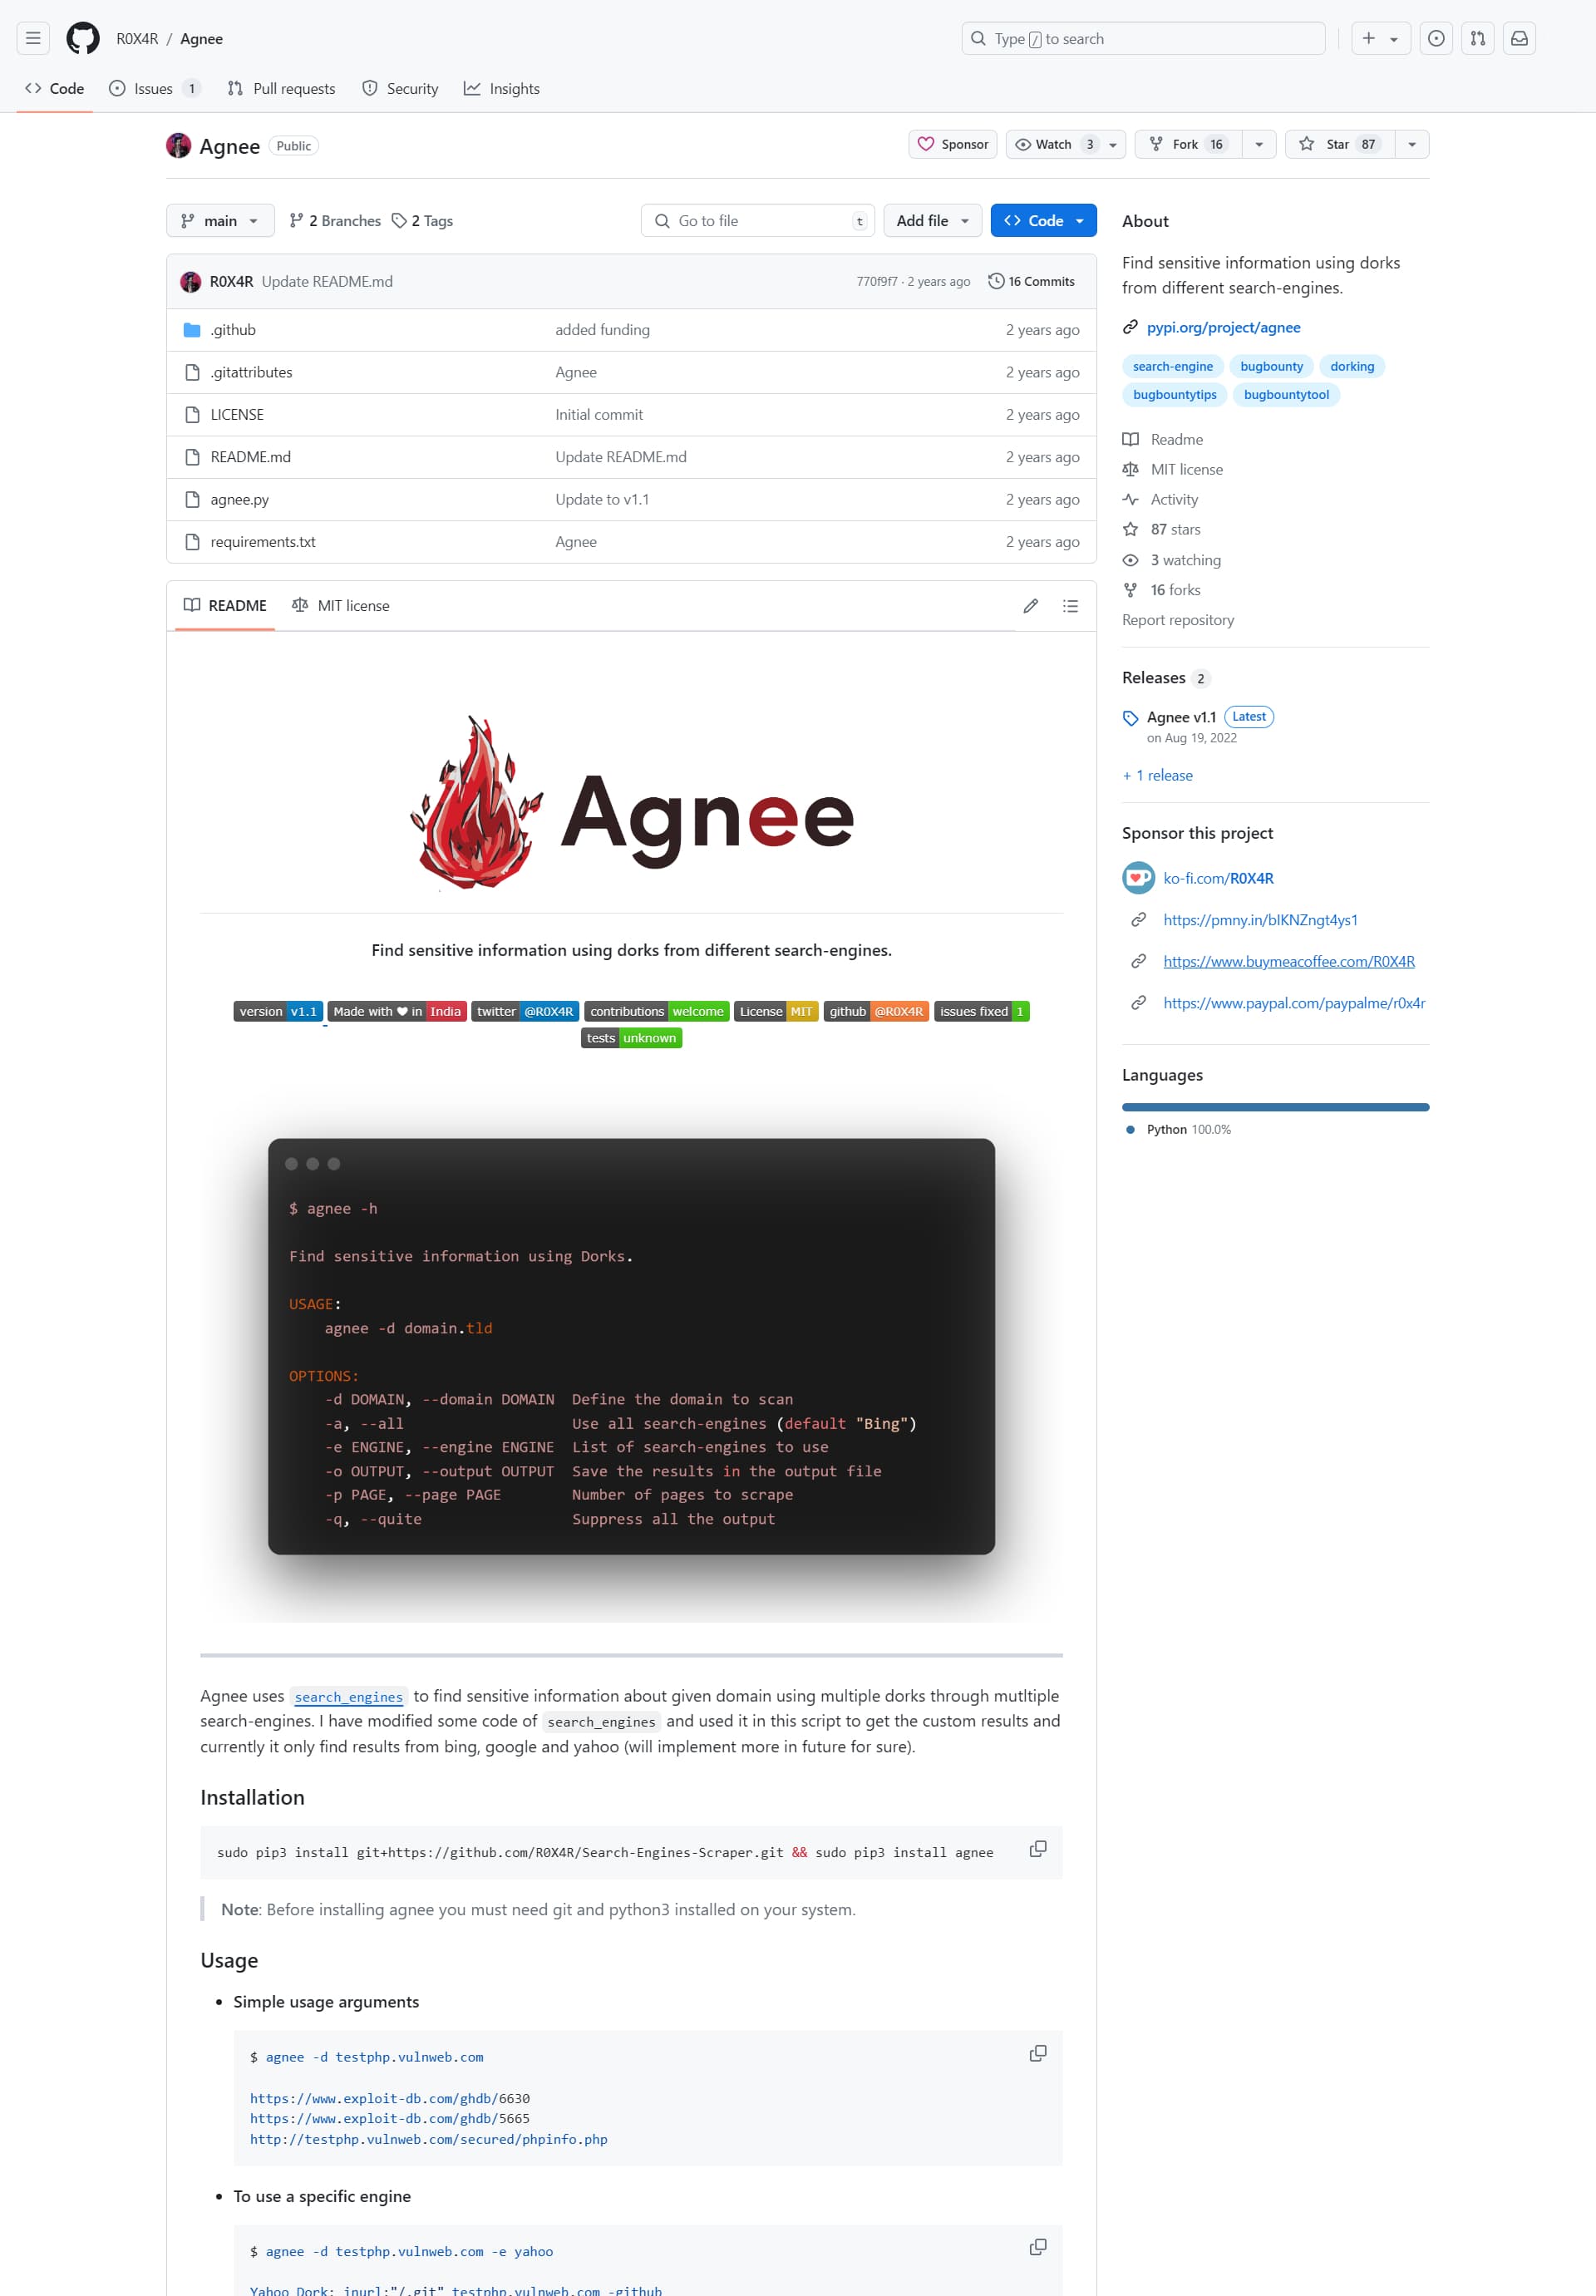
Agnee
Find sensitive information using dorks from different search-engines.
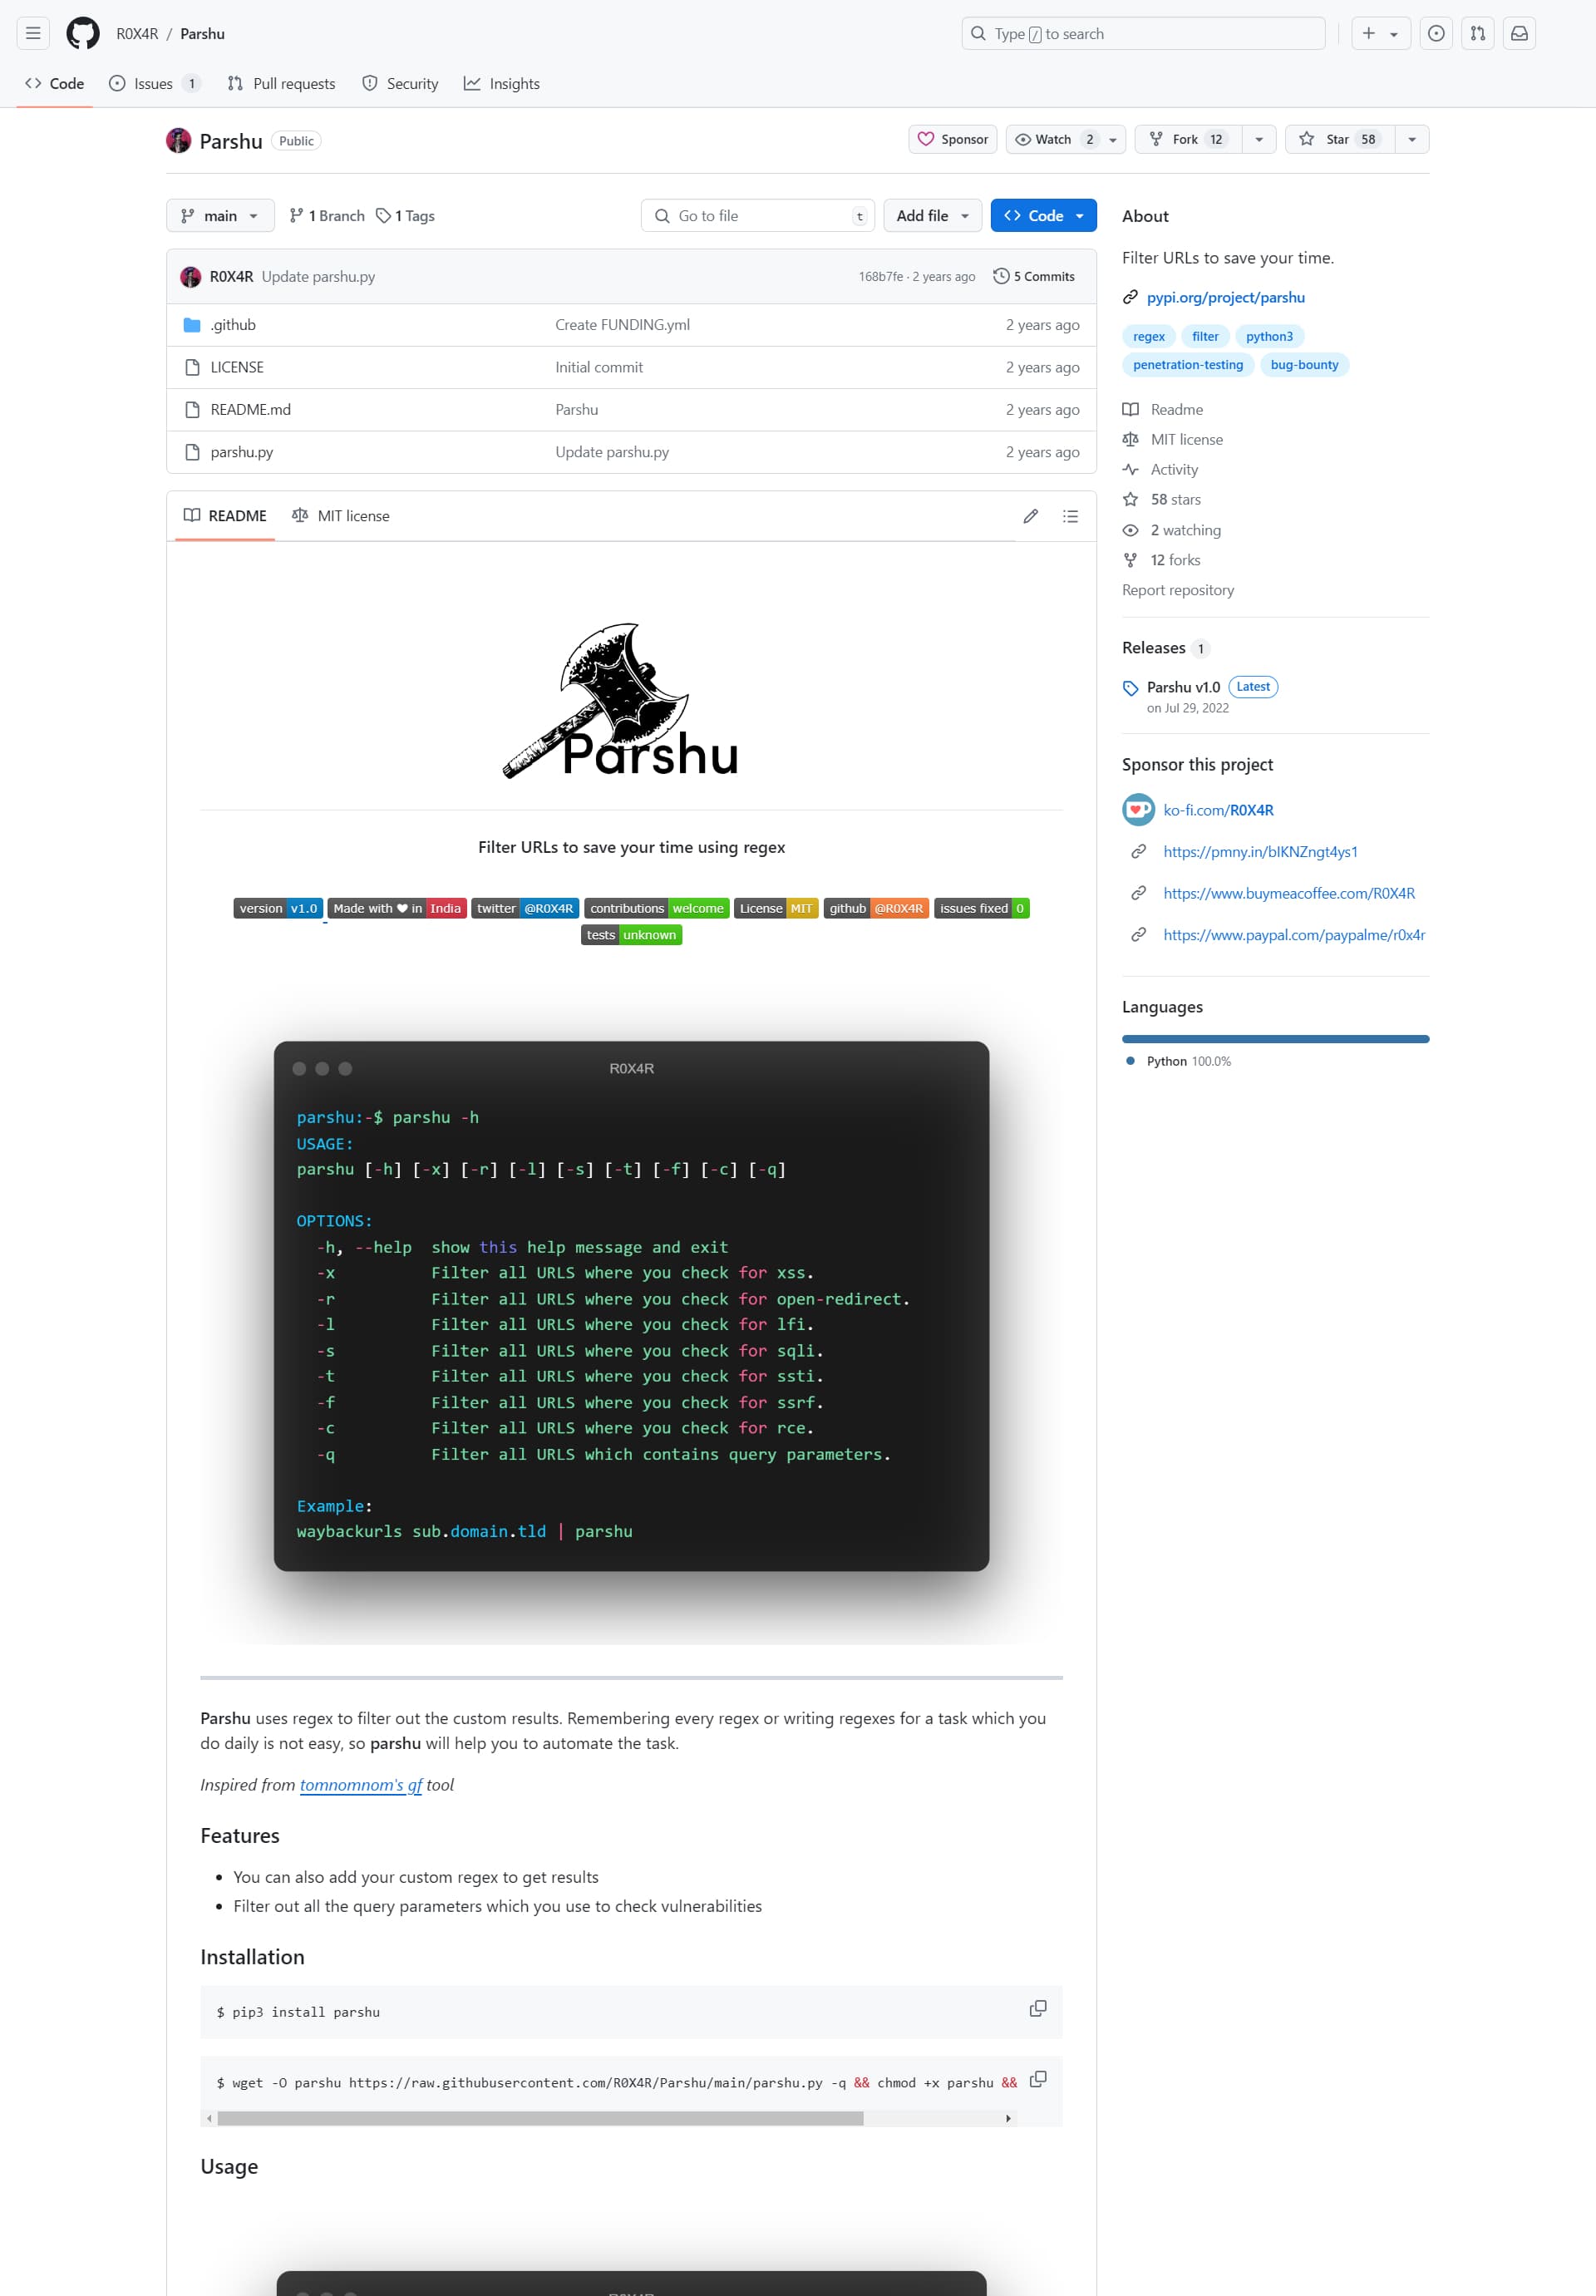
Parshu
Filter URLs to save your time using regex
Journey & Credentials
CyberZone Certified Network Administration (CZCNA)
Cyber Zone Technologies (P) Ltd.
CyberZone Certified Ethical Hacker
Cyber Zone Technologies (P) Ltd.
Cryptocurrency for Law Enforcement
FedVTE
Linux Administration 101
LetsUpgrade
101 Coding
Fortinet
NSE Level 1: Certified Associate
Fortinet
CybHER
Telangana State Police Department
Senior Secondary (Class XII)
SG Uchh Vidyalaya, Bhojpur
Junior Penetration Tester
eLearnSecurity (INE Security) Certified Junior Penetration Tester (eJPT)
500H Registered Yoga Teacher
Yoga Instructor Certification - Level II (Yoga Alliance)
Bachelor of Technology
B.Tech in CSE, Gurukul Kangri (Deemed to be University), FET, Haridwar
Skills & Tools

Burp Suite
HTTP Interception Proxy & Vulnerability Scanner
Nmap
Network Exploration & Security Port Auditing
OWASP ZAP
Dynamic Web Application Security Scanner
Dalfox
Parameter Analysis & XSS Scanning Engine

Metasploit
Penetration Testing System & Exploit Framework
Kali Linux
Offensive Security Platform & Tooling Suite
Kali Linux
Offensive Security Platform & Tooling Suite
Linux Internals
Kernel Architecture, Shells & Hardening
Bash
Offensive Shell Scripting & Recon Automation
Python
Custom Exploits, Bug Bounty Tools & Automation
Go Language
High-Performance Concurrency & Recon Scanners
Docker
Isolated Attack Labs & Container Environments
Docker
Isolated Attack Labs & Container Environments
Podman
Daemonless Rootless Container Management
Kubernetes
Cluster Orchestration & Cloud Infrastructure
AWS
Cloud Architecture, Identity IAM & Scalable Compute
Git
Distributed Version Control & Source Integrity

GitHub
Collaboration, Automated CI/CD & DevSecOps
GitHub
Collaboration, Automated CI/CD & DevSecOps
JavaScript
Dynamic Web Logic, Protocols & Browser Internals
React
Reactive UI Systems & Dynamic Architecture

Next.js
Fullstack App Router, SSR & Production Systems
Tailwind CSS
Modern Utility-First Styling & Component Design
Blogs and videos
GraphQL IDOR leads to information disclosure
While doing recon for redacted.com (A private program and as per their privacy policies, I cannot disclose their name), I found that the web app is using GraphQL for their API Management. So, I firstly tried Introspection Query to extract sensitive information.After passing the query I saw a field called Users, so I pass
GraphQL introspection leads to sensitive data disclosure
For Discovering this bug, I learned the fundamentals of GraphQL for at least 5–6 hours and read all other relevant bug reports, especially Namhamsec’s GraphQL CTF Challenge. After that, I saw a new program on Bugcrowd, so I participated in it.They gave me a domain [let’s take the domain as example.com because the vulnerability hasn’t fixed yet], i.e.example.com.
Introduction to Blind XSS
Last year I was scrolling my LinkedIn Profile feeds suddenly a post came in front of me. In that post, a Bug Hunter posted his PoC about how he found Blind-XSS in Spotify. I was surprised after hearing about BXSS. I was surprised at that moment after watching that there is another category of XSS which is known as BLIND XSS.
Learn with @R0X4R: Recon Automation & How To Approach For Help
In this video, Eshan Singh (@r0x4r) has shown his way of recon and which tool he uses to automate the process also he has explained how to approach another researcher for help.
Master FFUF for Bug Bounty
FFUF is a great tool for fuzzing. It is a fast web fuzzer written in Go. It is used to fuzz parameters, headers, and other parts of a web application. It is a great tool for bug bounty hunters and penetration testers. It is a very fast fuzzer. It is used to find hidden files and directories on a web server. It is a very powerful tool.
Bug Bounty POC: Oneplus
This video demonstrates a proof of concept (POC) for an XSS vulnerability found on the OnePlus website. It details the steps taken to discover and exploit the vulnerability, providing valuable insights for security enthusiasts.
Escalate Open-redirection into XSS
This video shows how an open-redirection vulnerability can be escalated into an XSS attack. It provides a step-by-step guide on finding the open-redirection issue and exploiting it for XSS, offering useful information for security researchers.